◆
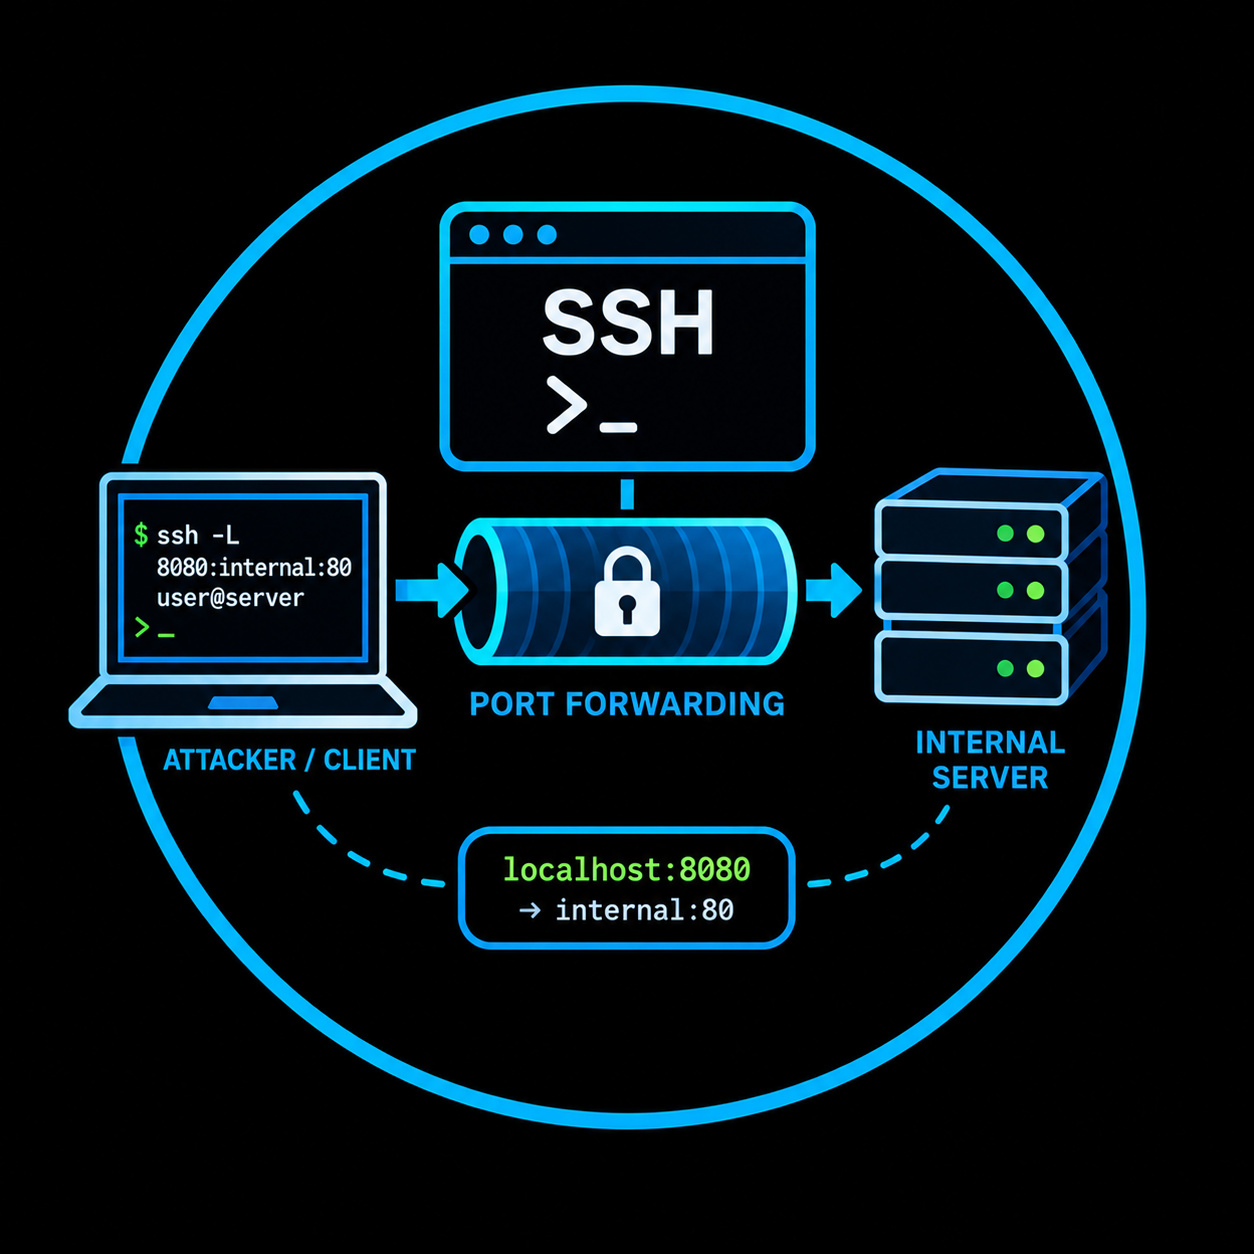
Pivoting with SSH Port Forwarding
How SSH tunnels let an attacker pivot through a compromised host, reach internal services invisible from the outside, and exfiltrate data through encrypted channels that blend with legitimate traffic.
—20 min read
13 posts
How SSH tunnels let an attacker pivot through a compromised host, reach internal services invisible from the outside, and exfiltrate data through encrypted channels that blend with legitimate traffic.
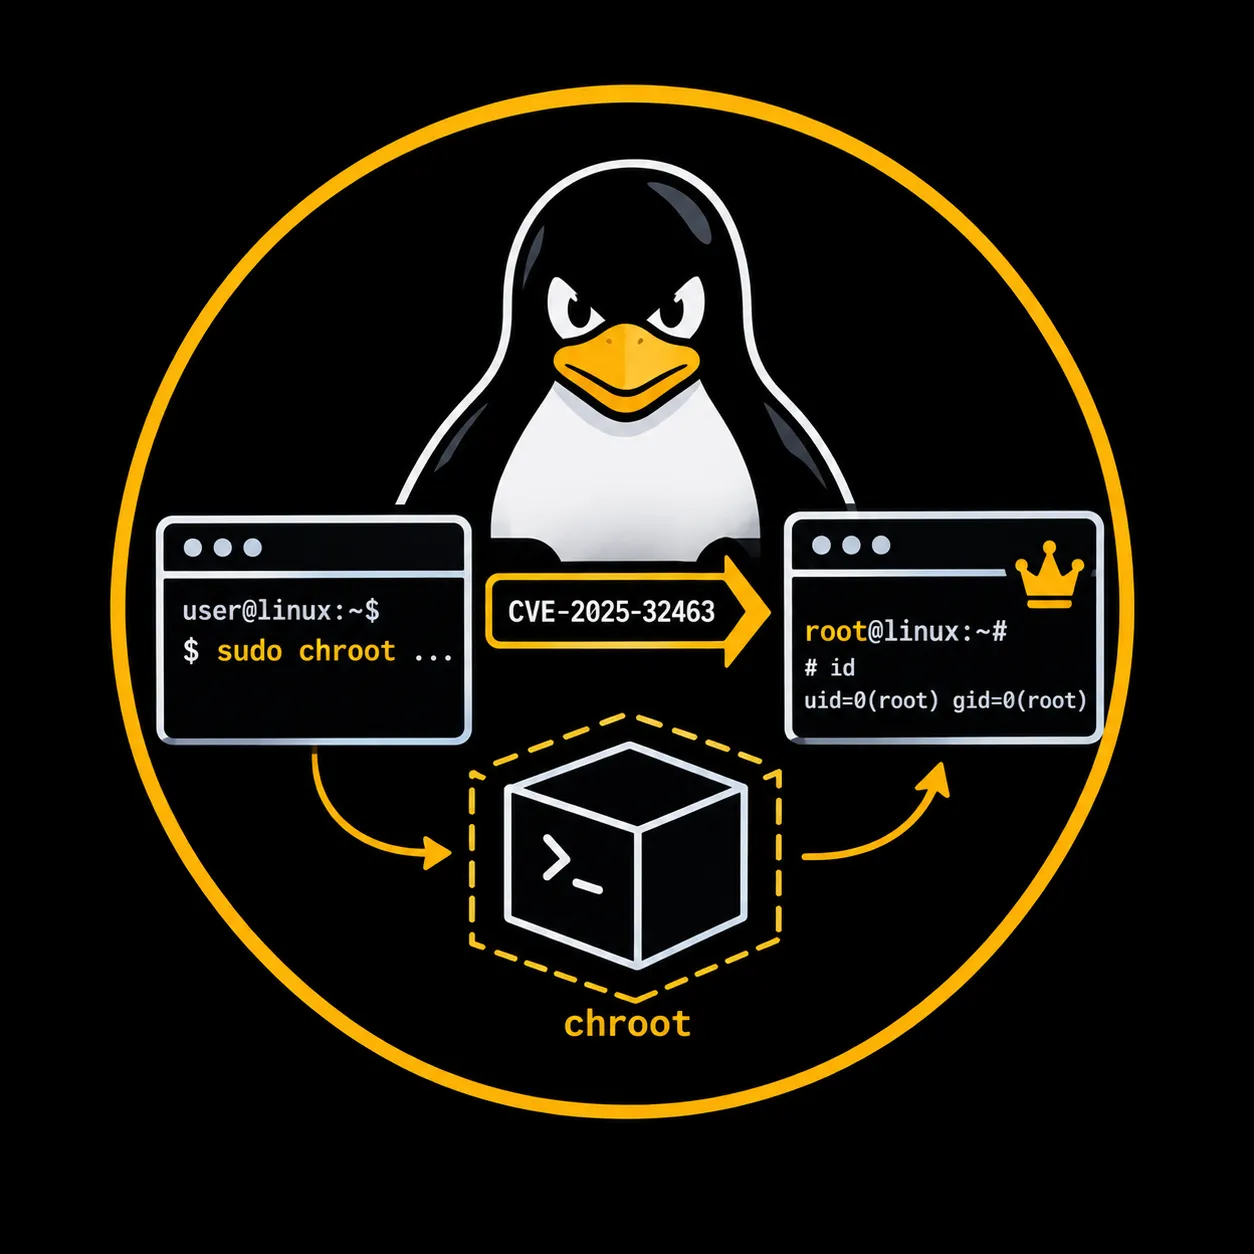
How a misplaced chroot call in sudo 1.9.14 through 1.9.17 lets any local user — with no sudoers rule and no password — trick glibc into loading an attacker-controlled shared library as root. Full root cause analysis, lab reproduction, exploitation, and detection.
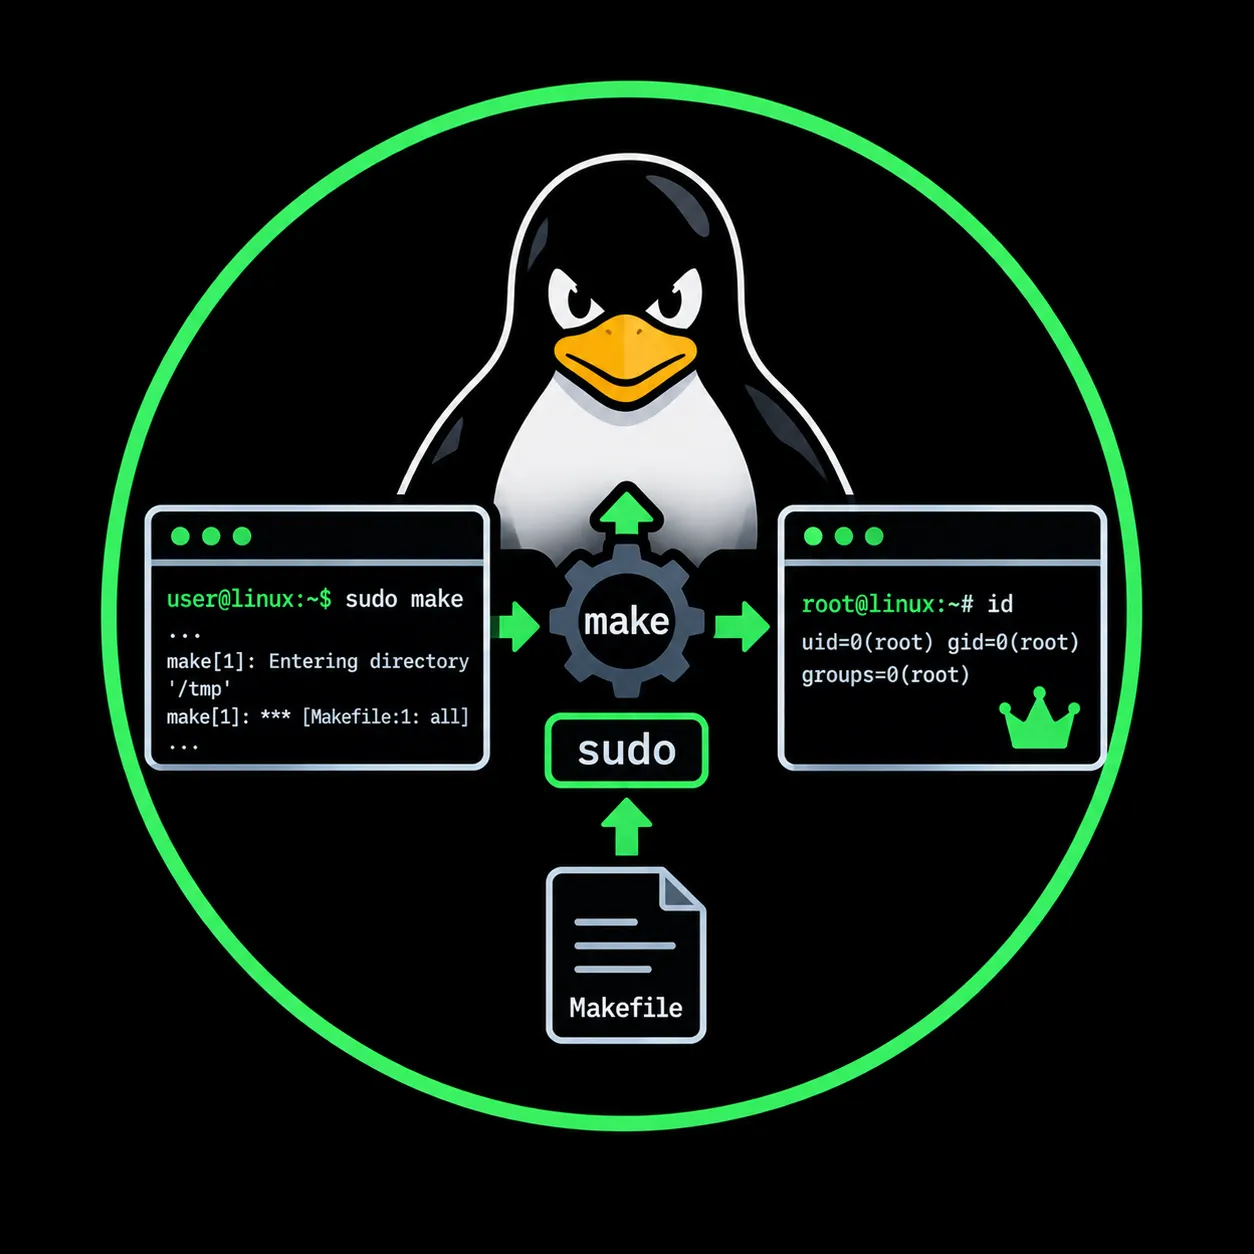
How GNU Make's --eval flag, $(shell), and $(file) functions turn a permissive sudo rule into full root access — shell execution, arbitrary file read, and arbitrary file write — with no vulnerability involved.
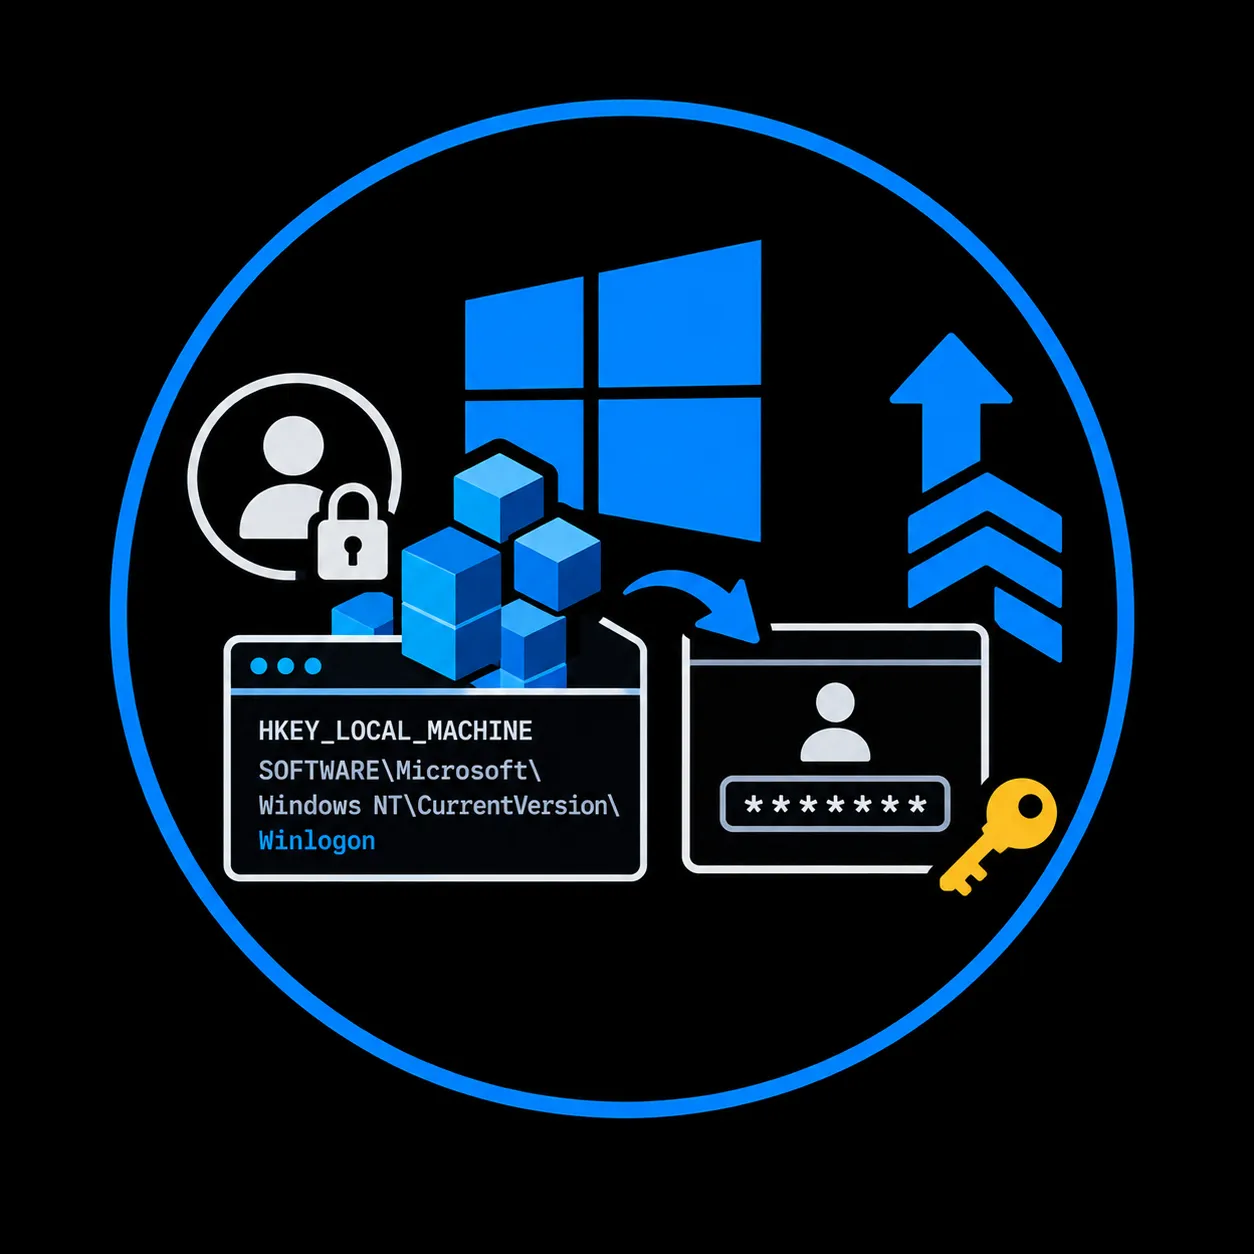
How Windows AutoLogon stores plaintext credentials in the registry under HKLM\SOFTWARE, why every authenticated user can read them, and how to turn a single reg query into privilege escalation or domain compromise during a penetration test.
How attackers inject executable code into server log files and combine it with Local File Inclusion to turn a read primitive into full remote code execution. Covering Apache, Nginx, SSH, FTP, and SMTP across Linux and Windows environments with lab demonstrations, realistic payloads, and detection strategies.
How a missing pair of quotation marks in a service's ImagePath lets a low privilege user place a binary that Windows executes as SYSTEM. Theory behind CreateProcess path resolution, lab setup, enumeration, and exploitation.
How attackers use Windows Task Scheduler to survive reboots, maintain access, and execute payloads as SYSTEM. Lab setup on a Domain Controller, multiple persistence paths via CMD and PowerShell.
How the PowerShell command history file silently records credentials in cleartext, where to find it, what leaks into it, and how to turn a history file into a privilege escalation during a pentest.
How any authenticated domain user can extract service account password hashes from Active Directory using legitimate Kerberos functionality, and crack them offline. Theory grounded in RFC 4120, lab setup, multiple exploitation paths, and cracking strategies.
From a low privileged domain user to NT AUTHORITY\SYSTEM by overwriting a service executable that weak file permissions left writable. Lab setup, enumeration, and exploitation.
How disabling Kerberos pre-authentication hands attackers an offline password crack with no credentials required. Lab setup, enumeration, exploitation, and offline cracking.
From Backup Operators to Domain Admin. Exploiting SeBackupPrivilege to bypass NTFS ACLs, extract ntds.dit or SAM hives, dump hashes offline, and Pass-the-Hash to SYSTEM.
Comprehensive guide to the Potato family of Windows privilege escalation exploits. From Hot Potato to Silver Potato, covering SeImpersonatePrivilege abuse, DCOM/RPC coercion, and NTLM relay techniques.