◆
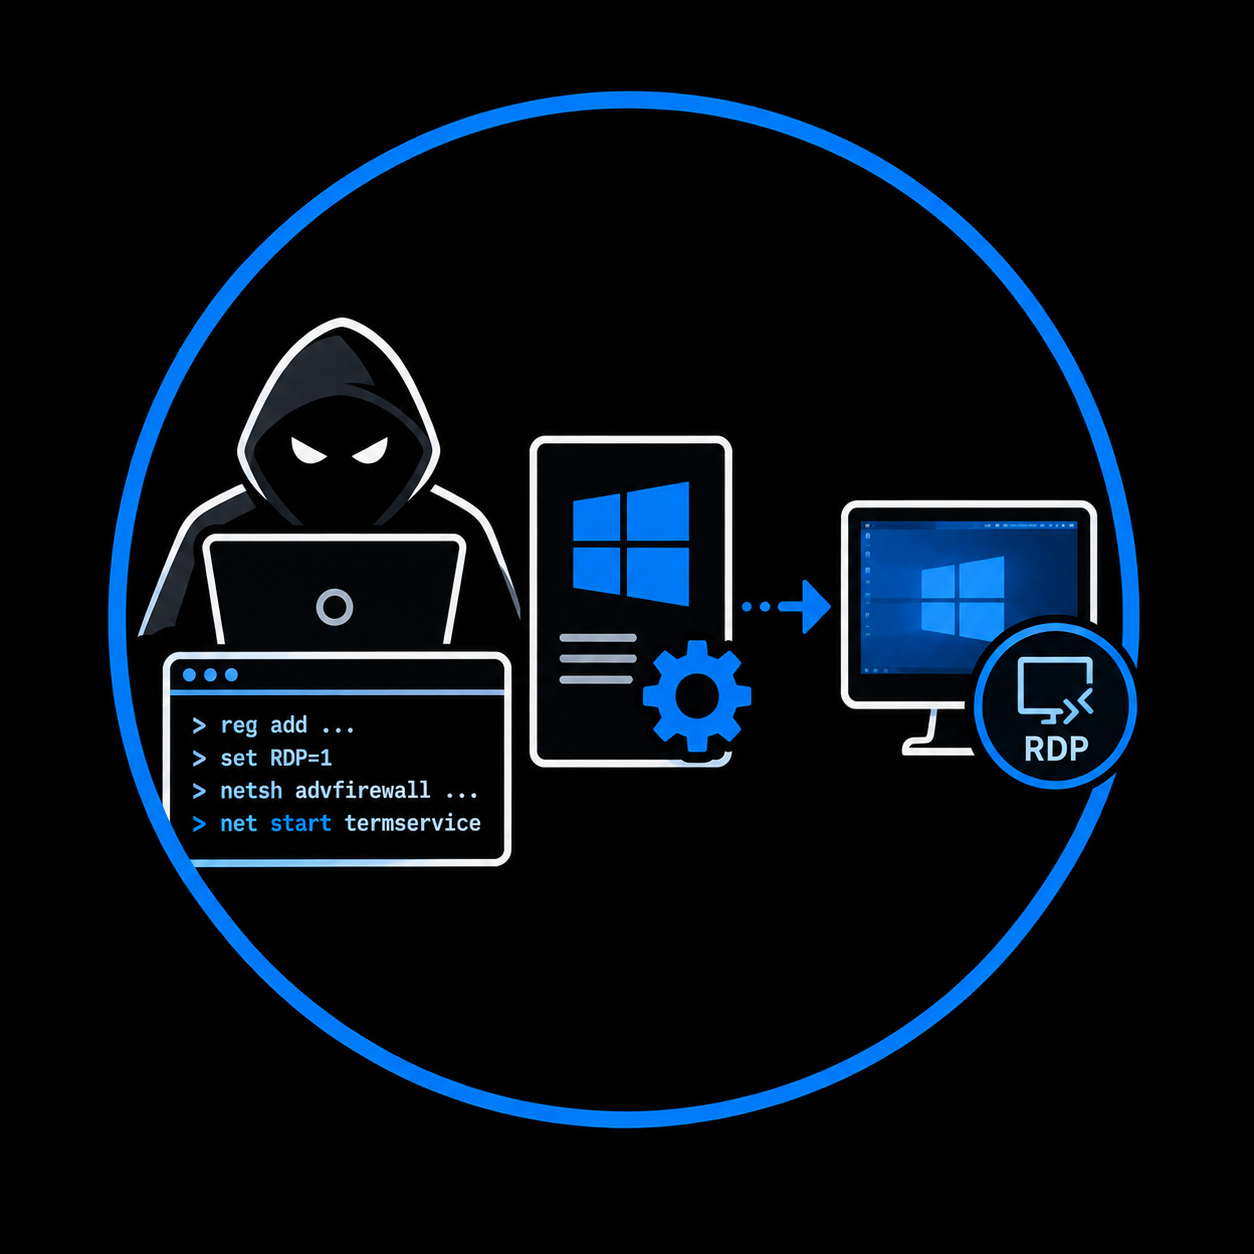
Windows Post-Exploitation: Enabling Remote Desktop (RDP)
After compromising a Windows host, an attacker with local administrator access can enable RDP by modifying a single registry value, opening the firewall, and optionally disabling NLA. This turns a command-line shell into full graphical access using built-in Windows functionality.
—10 min read